Barcode scanner flaw exposes warehouse cyber risks
Kaspersky researchers have identified a wireless barcode scanner vulnerability that could enable unauthorised access to warehouse networks and systems
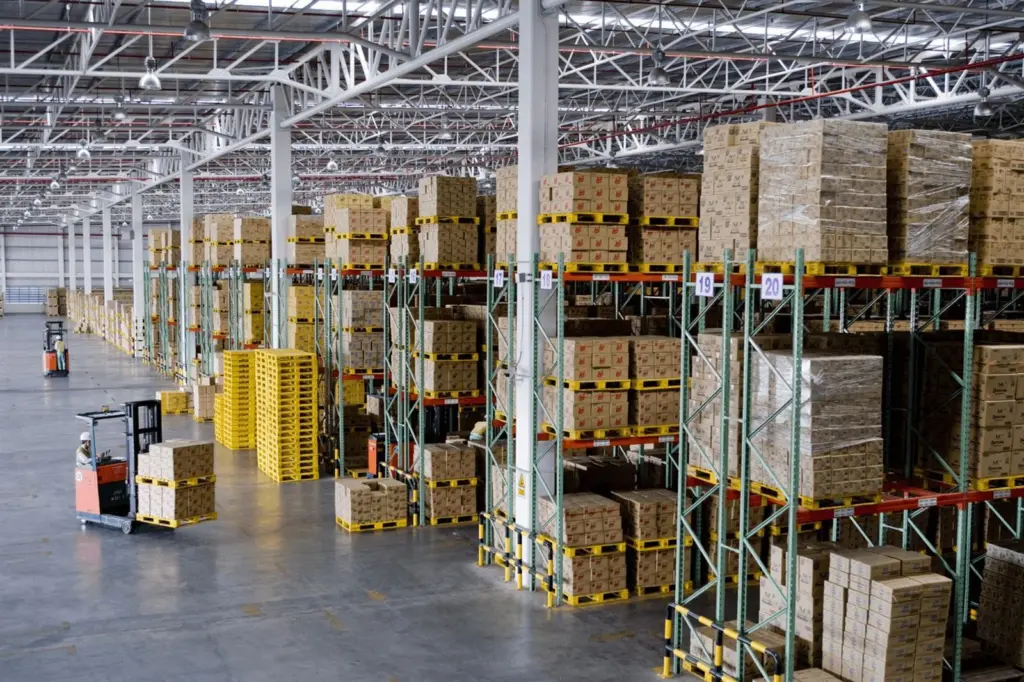
Cybersecurity researchers at Kaspersky have identified a potential attack vector involving wireless barcode scanners that could expose warehouse and retail networks to unauthorised access, raising concerns about security across increasingly connected supply chains.
The findings, presented at the Security Analyst Summit 2026 in Bali, emerged from an assessment of warehouse digital infrastructure. With global e-commerce sales exceeding $6 trillion, disruptions to logistics operations can carry significant financial and reputational consequences.
“Modern retail and logistics are profoundly digital, from enterprise-wide management platforms down to every device in a worker’s hands,” said Sergey Sidorov, head of Industrial Security Services at Kaspersky.
“This pervasive connectivity means that any technology at any tier can become an entry point for a cyberattack capable of destabilising the entire ecosystem – as our research shows, even a single barcode scanner.”
The vulnerability centres on a lack of authentication between handheld scanners and their base stations. According to Kaspersky, an attacker within wireless range could exploit the connection to inject keystrokes into a connected computer, potentially executing unauthorised commands without user interaction.
In a hypothetical attack scenario, an attacker could obtain a base station’s Bluetooth address by monitoring wireless traffic before sending a malicious payload. The base station would forward the simulated keystrokes to the connected workstation, potentially providing an initial foothold inside the warehouse network.
Researchers said the attack pattern was observed across devices from multiple vendors. Similar scenarios could potentially involve other equipment, including portable data terminals and thermal printers, creating risks for warehouse management systems and wider operational technology networks.
Kaspersky recommends verifying devices before connecting them to networks, disabling unused Bluetooth interfaces, enforcing strong authentication and segmenting networks to restrict unnecessary connections. Organisations should also apply security updates promptly, limit account permissions and regularly test potential attack paths.
The company offers industrial security assessments and its Kaspersky Industrial Cyber Security platform to help organisations identify vulnerabilities and improve visibility across connected infrastructure.
Related Articles
 CONTAINER & CARGO HANDLING
 BULK HANDLING
 CONTAINER & CARGO HANDLING